CodeRabbit Says Its AI Deep Scans Found 1,215 High or Critical Flaws in 1,125 Open Source Repositories

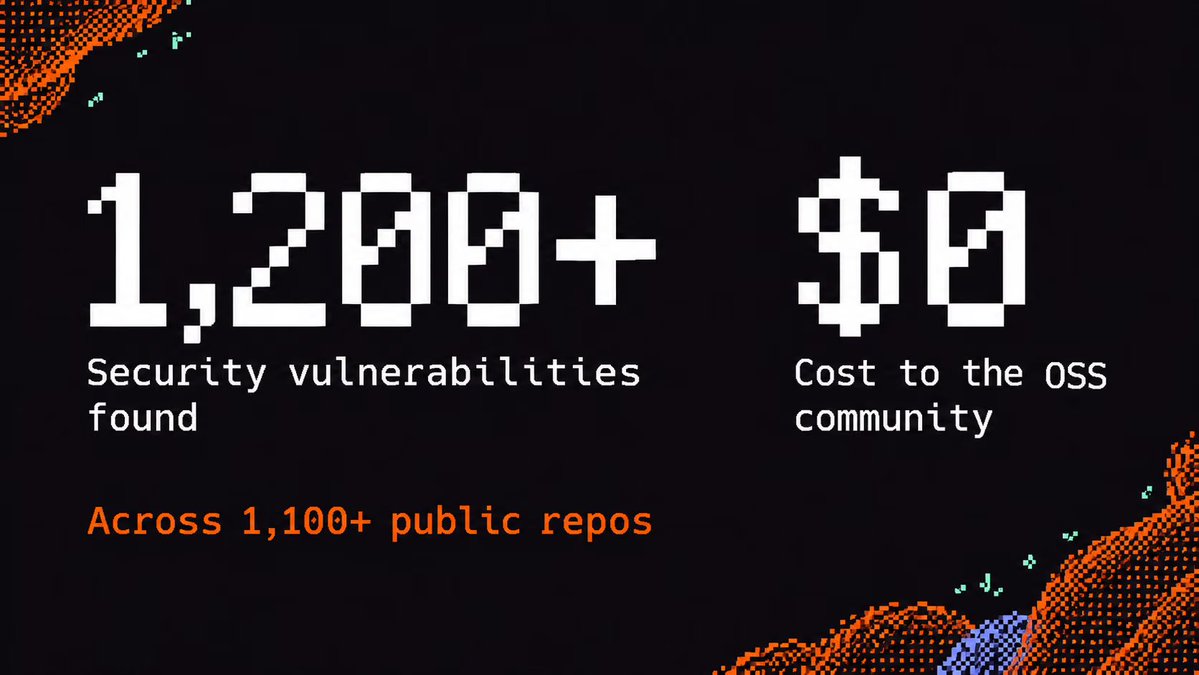
Attackers have AI agents probing open-source code 24/7 & we think maintainers should too! CodeRabbit ran Deep Scans on 1,125 public repos with 1,215 high or critical findings, 75 of which are already fixed. Your first Deep Scan is on us, up to $1K for orgs with 2+ people.
Context
It shows AI agents can now hunt security bugs across open source code at scale, while only a small share of what they find has been fixed so far.
CodeRabbit is an AI code review company. Deep Scan is part of its CodeRabbit Secure product and checks a whole repository, including older code, rather than only the latest change. On November 13 the company published results from a campaign that scanned public repositories at no cost to maintainers.
Deep dive
CodeRabbit says Deep Scans run between October 23 and November 3, 2026 on 1,125 public repositories found 1,215 high or critical security findings, 1,200 rated high and 15 critical. The company says at least 75 have been fixed so far, about 6% of the total.
According to its blog post, Deep Scan works in four stages. It maps a repository's entry points, trust boundaries and access controls, follows code paths to hunt for suspected flaws, and then hands each finding to a separate verifier that reopens the cited code and checks whether the flaw is reachable and whether safeguards already exist. For supported findings, a Fix with AI option drafts a patch for a developer to review and merge.
The company lists the most common problems as missing ownership checks, where an endpoint checks that a user is signed in but not that they may access a specific record, along with cross site scripting, weak identity checks, unsafe file path handling, sessions that stay valid after they should expire, and information exposure. The post names one project whose creator, Herrington Darkholme, said proving a vulnerability before flagging it makes each finding more actionable.
The post also offers open source projects with two or more members a free first Deep Scan worth up to $1,000. The findings are CodeRabbit's own figures and were not independently verified in the posts scanned.
What to expect next
Watch how many of the remaining findings maintainers fix, since only 75 of 1,215 were reported fixed when the results came out. Independent checks of false positive rates would show how reliable the verifier stage is. Other AI security tools are likely to publish similar large scale scans, which could put more pressure on volunteer maintainers who must review and patch each report.